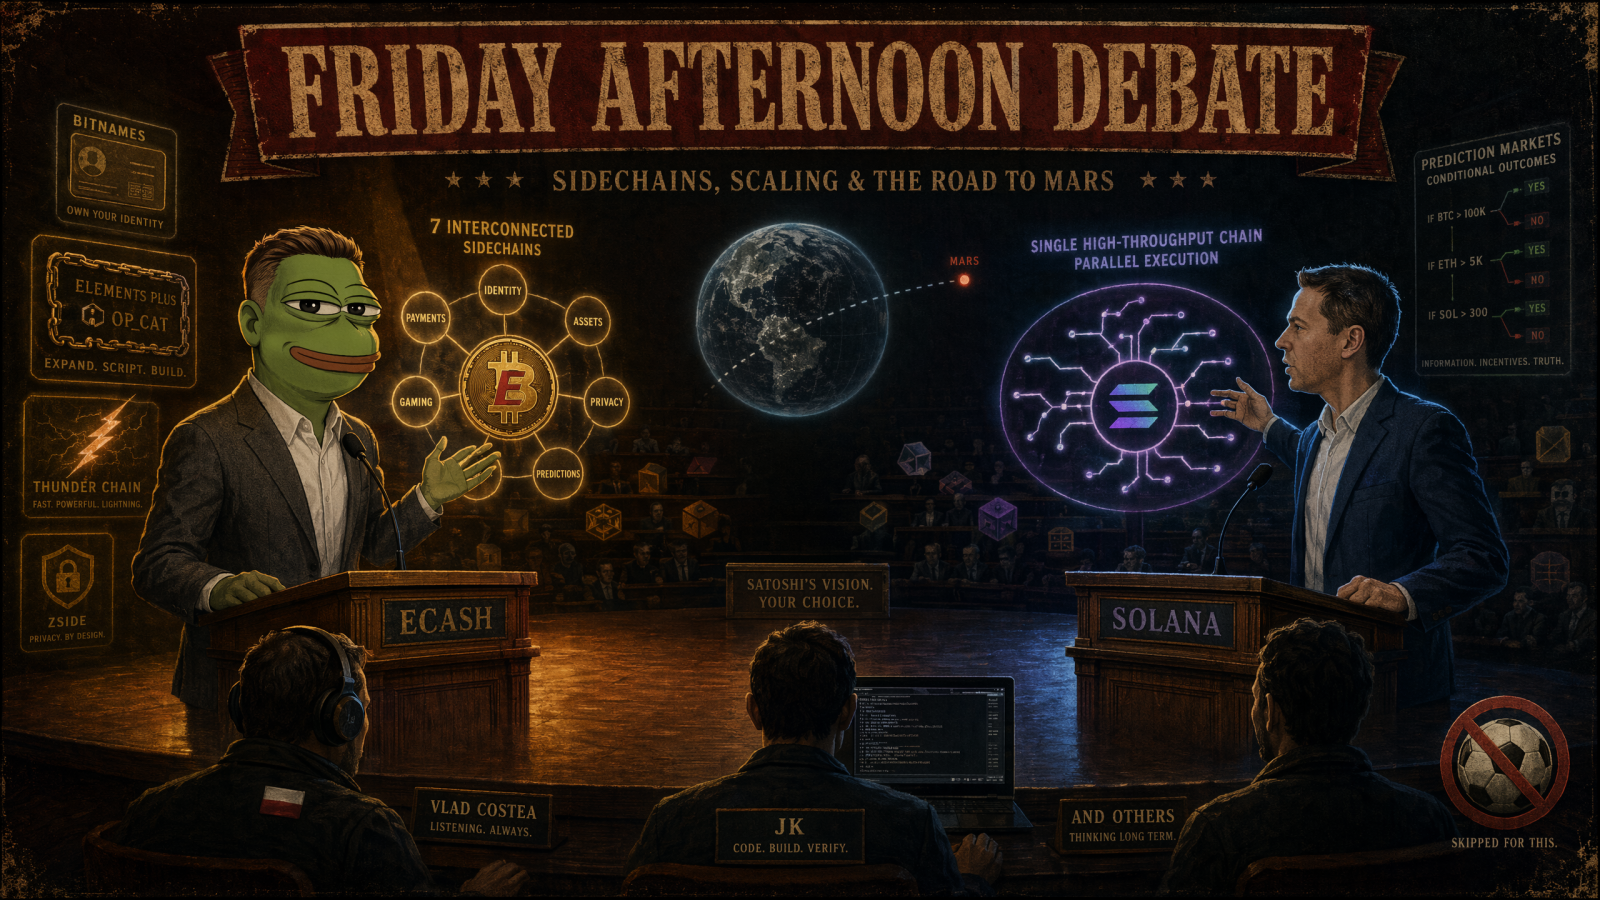
Paul Sztorc's June 19th Twitter Space: Silent Payments, BitNames, and a Deep Debate with Justin Bons
On a Friday afternoon, while the USA World Cup games are taking place in parallel, it's probably not the best time to host a two-hour Twitter Space about drivechains. But Paul Sztorc went ahead anyway, and the result was one of the more substantive conversations of the entire run-up to the August 2026 Ecash launch. Joined by Vlad Costea, JK, Justin Bons, and others, the session ranged from new wallet privacy features to Mars colony payments to a genuinely fascinating disagreement about what decentralization even means. Below, is a summary of what was discussed.
Silent Payments and BIP 47 Are Coming to Ecash
The first announcement was a technical one. Sztorc confirmed that Ecash will ship with silent payments and BIP 47 support, meaning users will not have to deal with traditional Bitcoin-style reusable addresses. He framed this as long overdue, noting that the original push to eliminate human-readable addresses dates back to 2014 and never made it across the finish line on Bitcoin itself. The pitch is simple: you should be able to chat with someone and send money directly to their screen name, without ever copying and pasting a string of characters.
The second bug bounty round is also underway, with the first round having uncovered enough issues that most of the team's attention has been on patching rather than shipping new features.
Clarifying the ECX Solana Token Math
Sztorc spent a few minutes addressing a recurring confusion about the Solana-side meme token. Some people have argued that because the top 15 wallets hold roughly half of the supply, only those 15 holders benefit from the redemption mechanism. Sztorc explained why this is wrong. If the top 15 own 50 percent of the market cap, they only receive 50 percent of the redemption pool. To collect more, they have to buy from everyone else. So every coin retains real value regardless of whether the holder is in the top 15. He admitted some frustration that the question keeps coming up despite the logic being straightforward.
The Elements Plus Sidechain and the Coming Brain Drain
Vlad steered the discussion toward what is actually being built. The Elements Plus sidechain stood out as the most interesting near-term addition. It will include OP_CAT, OP_CTV, and a range of additional opcodes that Blockstream originally enabled in their Elements platform. Sztorc described OP_CAT as the kind of tiny primitive that builders like Robin Linus and Super Testnet can use to construct elaborate cryptographic machinery, citing Starkware as an example of a project that only needed OP_CAT to do real work.
The broader point was about brain drain. Sztorc believes that builders who have spent years trying to make things work on Bitcoin within a hostile cultural environment will gravitate to Ecash sidechains once there is real money flowing and real freedom to ship. He drew a contrast with hired developers, who in his view tend to be the lower quality ones who lie about progress. The real builders just want a few small tools and the permission to experiment.
He also offered a notable aside about Michael Saylor. If Saylor gets liquidated, which Sztorc considers a real possibility, Bitcoin may culturally recover. That outcome would be bad for Ecash but potentially good for the world. Either way, he sees the next several months as a window in which serious developers can be drawn into the Ecash ecosystem.
Vlad noted the irony that every chain wants what it does not have. Bitcoin Cash worked hard to add DeFi-style capabilities. The Ethereum side is now publishing essays admitting that payments were the thing that mattered all along. Sztorc's response was that the drivechain model lets every experiment run in parallel, with the surviving ones earning real fees and the failures dying off cleanly.
BitNames and the Future of Online Identity
A long stretch of the conversation focused on BitNames, the identity-and-naming sidechain. Sztorc has ambitious plans here. The vision is that a user owns one name, and that name does everything. Login to Instagram or TikTok, messaging across platforms, payments, all routed through one human-readable handle. He wants to onboard non-crypto users by selling them a name for 20 dollars on a credit card, giving them 10 dollars worth of spending credit to play with, and walking them through generating their own wallet, possibly using shuffled playing cards as the entropy source, before transferring the name to that new wallet.
A key feature is that every BitName automatically comes with a randomly assigned phone-number-like identifier. The economic design includes paid introductions. If you want to message someone cold, you pay a small fee. After the first message, you can keep chatting until they block you, at which point you would have to pay again. Sztorc framed this as appropriate for an era of information abundance, where attention is the scarce resource rather than the message itself.
JK pressed on what wallet integration would look like and how BitNames could resolve to addresses across multiple sidechains. Sztorc described it as essentially a key-value store with arbitrary record types, similar to DNS TXT and A records. A BitName lookup could return a BIP 47 reusable payment code, a reusable Z address for Zside, and any other relevant data. He also walked through how BitNames could eventually interoperate with ICANN while respecting existing property rights to domains like google.com.
When Contracts Attack: The Theory Behind Topical Sidechains
JK raised a deeper question about what happens when multiple BitNames sidechains exist or when external contracts try to reference state from a BitNames chain. This led to Sztorc revisiting his "when contracts attack" framework, which he wrote about years ago and has watched play out repeatedly in practice.
The core argument is that miners ultimately serve as a court of last resort. If parasitic chains spring up to copy or interfere with a legitimate one, miners can simply refuse to advance them, since their revenue depends on the productive chain succeeding. Sztorc compared this to a traffic gridlock dissolved by a police officer ordering cars around. Even the last car to leave the intersection benefits from someone with authority overriding the standoff.
He also explained why topical sidechains beat overlay protocols like Counterparty. On a dedicated chain, state can be enforced efficiently. A BitNames node maintains an alphabetical tree of registered names and rejects double-registrations. On an overlay protocol, the same OP_RETURN-style data can produce contradictory state, because the base layer accepts everything and the overlay has to reconcile it after the fact. The result is that overlays force users to download more data to verify anything, while topical chains preserve efficient lightweight verification.
A Tor-Replacement Sidechain That Almost Was
Sztorc spent a few minutes describing an idea he had sketched out years ago but never published in full: a paid VPN-style sidechain that would compete with Tor by actually compensating relay nodes. The problem with Tor, in his framing, is that it is communist. Everyone runs it for free, so capacity is limited and speed is poor. A paid system could be fast because users would purchase credits to have their packets forwarded, and nodes would earn money in the background while their owners walked their dogs.
The interesting technical wrinkle was the audit mechanism. Users would send some packets to themselves and check whether relays were honoring the forwarding contract. Because traffic is anonymous, relays would not know which packets were tests. Sztorc said he has the design written down on paper somewhere but has not productized it.
The Mars Sidechain Proposal
Vlad floated a half-serious idea about a Mars-themed sidechain designed for interplanetary payments, with block times long enough to accommodate the eight-to-twenty-two minute communication delay between Earth and Mars. Sztorc gently shot it down. You do not need a drivechain for slower blocks. You can simply wait for more confirmations. He warned against the early-Ethereum tendency to propose a smart contract for everything, including imagined use cases like cars on the highway paying each other to change lanes. Cute, but a category error.
The Justin Bons Conversation: Sharding, Speed, and Decentralization
The most analytically rich portion of the call came when Justin Bons joined. Bons, a longtime critic of Bitcoin maximalism who has moved through Bitcoin, Bitcoin Cash, Ethereum, and now Solana as his primary holdings, congratulated Sztorc on the Ecash project and immediately dove into substantive disagreements.
His first observation was that drivechains with merge mining look structurally similar to enshrined sharding. Sztorc partially agreed but emphasized that drivechain L2s are explicitly opt-in for L1 validators, preserving the data availability properties that small blockers care about. Bons argued that if you are going to enshrine the relationship anyway, you might as well change the L1 to support faster blocks and larger block sizes, since the chain would be more capable as a result.
Sztorc pushed back hard on this. The Ecash L1 must be a near-perfect copy of Bitcoin Core specifically to avoid muddying the experimental design. The August fork should be a referendum on BIP 300 itself, not a referendum on every parameter that could be tweaked. If you change the block time and the block size at the same time, you can no longer attribute outcomes cleanly to any one design decision. He acknowledged this is partly a marketing argument, but argued it is also a discipline that makes the project legible.
The two then sparred over whether ten-minute block times are objectively bad. Bons argued that fast block times are essential for DeFi use cases like perpetual exchanges, which is where most fee revenue in crypto comes from now. Sztorc responded that fast blocks are a clumsy way to achieve speed. A better approach is staking-based instant confirmation on top of slow base-layer blocks. He also pointed out that ten-minute blocks produce a beautifully compact SPV experience, roughly four megabytes of headers per year, which scales linearly with block frequency. Faster blocks make SPV proportionally more expensive.
Bons countered that modern phones can handle larger header sets without difficulty, and that pruning addresses much of the bandwidth concern anyway. The disagreement was respectful but unresolved.
The Blind Merge Mining Explanation
Bons asked Sztorc to explain how fees flow from L2s back to L1 miners. The answer was one of the cleanest expositions of blind merge mining Sztorc has offered in this format.
Each L1 block has a slot reserved for the hash of each sidechain's latest block. L2 nodes compete to construct the block that gets recorded in that slot. They do this by paying L1 miners in L1 coins, with the bid set just below the value they expect to extract from running the L2 (transaction fees plus any MEV, minus operational costs and block maturity risk). Because the bids happen in L1 coins, the L1 miners do not need to know or care about anything happening on the L2. They just see one transaction with a high fee attached.
Bons probed on whether this would prevent an L2 from siphoning fees back to a founding company, similar to how Solana DEXes route fees back to their operators. Sztorc said the design assumes economic incentives rather than enforcement: if an L2 keeps too much value for itself, its bids in L1 will be lower, and miners can simply refuse to advance it. The system self-corrects through the same competitive pressure that makes any market work.
Bons noted, accurately, that this is a fee market layered on top of a fee market. Sztorc agreed and said this is preferable to encoding everything in rigid equations, because real-world conditions are too variable for static formulas to capture.
The Decentralization Debate: What does it even mean?!
The conversation peaked with a back-and-forth about what decentralization actually means. Bons argued that Solana today is more decentralized than Bitcoin across most metrics: more validators, broader geographic distribution, more diverse client implementations. He defined decentralization as the distribution of power, framing it as an evolution of the separation of powers in political theory.
Sztorc was sympathetic to that framing but resisted simple metrics. He pointed out that hash rate is not actually a property of a node, since the same ASIC can be pointed at any node. He has long preferred to break decentralization into sub-components rather than treat it as a single dimension.
JK weighed in with a different angle. Constraints, he argued, are themselves a source of decentralization. Software written for 100,000 Raspberry Pis is forced to be lean, while software running on 10,000 high-powered validators tends to accumulate complexity and inefficiency. He framed this as the difference between fragile and antifragile systems. Bons disagreed that the trade-off is necessary, arguing that you can have both efficient software and powerful hardware.
The unresolved philosophical question hanging over the exchange was whether decentralization is intrinsically valuable or whether it only matters insofar as it produces censorship resistance and credible neutrality. Bons leaned toward the latter. Sztorc has spent his career protecting the right of people to disagree about exactly that.
Closing Thoughts on DeFi and Prediction Markets
In the final stretch, JK asked Sztorc what kind of DeFi he hopes will eventually emerge on Ecash. The answer was prediction markets, of course. Sztorc walked through what he sees as the most underexplored design: hybrid conditional markets that let traders express views like "if the Fed cuts rates, what will inflation be?" or "if the Republicans lose power in 2028, what will GDP be?" Polymarket and Kalshi have not implemented these despite Sztorc writing about them for over a decade. He believes the demand is enormous and that the existence of such markets would change how policy and economics are discussed in public.
He was politely dismissive of Ethereum-style DeFi, comparing it to ordinals: nice that real users and fees exist, but ultimately a thin layer over speculation. Prediction markets, by contrast, produce information as their output, which can be settled cleanly on-chain without anyone needing to ship physical commodities.
What This Call Revealed
This was a different kind of Space from the prior weeks. There was no major announcement, no heated confrontation, no breaking news. Instead it was Sztorc in his element: explaining the design choices behind BIP 300, defending blind merge mining against intelligent pushback, sketching ambitious applications like BitNames and paid VPN networks, and engaging seriously with a sophisticated critic who disagrees with him about almost everything except the goal of building useful systems.
The most telling exchange may have been the one about L1 changes. Bons made a reasonable case that the Ecash L1 should have faster blocks and bigger blocks to support the kinds of applications driving crypto revenue today. Sztorc declined, not because the changes would be technically wrong, but because making them would compromise the cleanliness of the experiment. The August fork is a single hypothesis test: does BIP 300 work in production? Everything else has to be held constant for the answer to be meaningful.
Whether that discipline holds through launch is the open question. But the project sounds increasingly mature, with the difficult conversations happening publicly and the cultural framing settling into something more confident than urgent.